Exploit Testing

The last few weeks of the year are usually the best to start testing systems at my current job. We currently have the following security measures in place:

Cisco Firewalls
Juniper Firewalls
Cisco IPS
Cisco Switches with ACLs on each VLAN
Secured Syslog Server
Secured Snort (IDS) Server
McAfee Antivirus
Windows Updates*

*Windows Updates are not forced on the Dev Team or Server Farms – Those updates are installed manually usually once a quarter (after testing).

Seeing as it’s Tuesday December 28th, I had some free time to test out the Antivirus installed on each system. Most exploits today are not actually against the OS (Microsoft has done a pretty decent job lately with security issues, even with that huge DLL issue) and are instead targeting 3rd party applications.

What do you consider a 3rd party application? The biggest two are:

Adobe (PDF Reader, Flash Player)
Sun (Java)

So I decided to test in my VMWare environment using the latest and greatest updates for Windows XP. Why did I choose XP over 7? Looking over my log files I see that most visitors to my site include XP users. XP has also been around long enough to get all the kinks worked out. And finally, I chose to use PDF/Java exploits, so the OS doesn’t really matter as much.

Please don’t visit these websites unless you know what you’re doing. And I used smartscan/quickscan whenever possible.

Test 1 (Nod32/Threatfire):

Windows XP Pro SP3
Fully Updated 12.28.2010
Internet Explorer 8.0.6001.18702
Nod32 Antivirus 4.2.67.10 5739
Threatfire 4.7.0.17
Secunia PSI 2.0.0.1002 100%
Adobe Flash Player 10 ActiveX 10.1.102.64
Java 6 Update 23 6.0.230
Malwarebytes Anti-Malware 1.50.1.1100 5408

cryyahoo.info/tre/boba.exe
Blocked by Nod – Downloaded Java (c:\doc and set\Administratorupdate665744669.exe) **PDF/Java/Trojan**

expa82.co.cc/bl2/
Blocked by Nod **Trojan**

1.oresmir.co.cc/1/load.php?spl=mdac
IE labeled download as unsafe, Cleaned by Nod **Trojan**

marinada3.com/77/throatnut.php
Blocked by IE – Java exploit blocked by Nod (Freezes IE) **Java/Trojan**

Malwarebytes:
Objects infected: 3 (3 are non-infection related)

Verdict:
Clean system, difficult to infect on accident.
Performed scan by Nod32/Threatfire – nothing found.

Test 2 (McAfee):

Windows XP Pro SP3
Fully Updated 12.28.2010
Internet Explorer 8.0.6001.18702
McAfee VirusScan Enterprise 8.7i 6210.0000
Adobe Flash Player 10 ActiveX 10.1.102.64
Java 6 Update 23 6.0.230
Malwarebytes Anti-Malware 1.50.1.1100 5408

cryyahoo.info/tre/boba.exe
Allowed to download – no extra processes

expa82.co.cc/bl2/
Allowed to load page – no extra processes

1.oresmir.co.cc/1/load.php?spl=mdac
IE labeled download as unsafe, allowed to install (load.exe, csrss in temp folder)

marinada3.com/77/throatnut.php
Blocked by IE – no extra processes

Malwarebytes:
Objects infected: 14 (3 are non-infection related)

Verdict:
CSRSS.EXE running as SYSTEM and Administrator. Infected system.
Performed scan by McAfee – nothing found.

Test 3 (McAfee/Threatfire):

Windows XP Pro SP3
Fully Updated 12.28.2010
Internet Explorer 8.0.6001.18702
McAfee VirusScan Enterprise 8.7i 6210.0000
Threatfire 4.7.0.17
Adobe Flash Player 10 ActiveX 10.1.102.64
Java 6 Update 23 6.0.230
Malwarebytes Anti-Malware 1.50.1.1100 5408

cryyahoo.info/tre/boba.exe
Allowed to load page – file would not download

expa82.co.cc/bl2/
Allowed to load page – no extra processes

1.oresmir.co.cc/1/load.php?spl=mdac
IE labeled download as unsafe, Threatfire detected and blocked the installation, then found and blocked load.exe

marinada3.com/77/throatnut.php
Blocked by IE – no extra processes

Malwarebytes:
Objects infected: 4 (3 are non-infection related)

Verdict:
Only infection file was located as a temporary internet file download and was not referenced in the registry. “Clean” system.
Performed scan by McAfee and Threatfire – nothing found.

Test 4 (Nod32):

Windows XP Pro SP3
Fully Updated 12.28.2010
Internet Explorer 8.0.6001.18702
Nod32 Antivirus 4.2.67.10 5739
Adobe Flash Player 10 ActiveX 10.1.102.64
Java 6 Update 23 6.0.230
Malwarebytes Anti-Malware 1.50.1.1100 5408

cryyahoo.info/tre/boba.exe
Blocked by Nod

expa82.co.cc/bl2/
Blocked by Nod

1.oresmir.co.cc/1/load.php?spl=mdac
IE labeled download as unsafe – Not found by Nod32

marinada3.com/77/throatnut.php
Blocked by IE – Java exploit blocked by Nod32

Malwarebytes:
Objects infected: 13 (3 are non-infection related)

Verdict:
Infected system, somewhat hard to infect on accident, but a definite possibility. CSRSS.exe is loading.
Performed scan by Nod32 – nothing found.
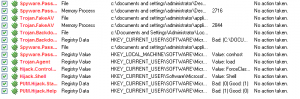
Test 5 (No AV):

Windows XP Pro SP3
Fully Updated 12.28.2010
Internet Explorer 8.0.6001.18702
Adobe Flash Player 10 ActiveX 10.1.102.64
Java 6 Update 23 6.0.230
Malwarebytes Anti-Malware 1.50.1.1100 5408

cryyahoo.info/tre/boba.exe
IE reported this site as BAD – File not found to download

expa82.co.cc/bl2/
Site loaded fine – no extra processes

1.oresmir.co.cc/1/load.php?spl=mdac
IE labeled download as unsafe – Saved and run successfully

marinada3.com/77/throatnut.php
Blocked by IE – Java exploit allowed to load – no additional processes

Malwarebytes: (google searches redirected to other websites, had to kill load.exe)
Objects infected: 14 (3 are non-infection related)

Verdict:
It’s always better to have some sort of antivirus software installed. So I can’t recommend this at all.

Test 6 (Microsoft Security Essentials MSE):

Windows XP Pro SP3
Fully Updated 12.28.2010
Internet Explorer 8.0.6001.18702
Adobe Flash Player 10 ActiveX 10.1.102.64
Java 6 Update 23 6.0.230
Malwarebytes Anti-Malware 1.50.1.1100 5408

cryyahoo.info/tre/boba.exe
IE reported this site as BAD – File not found to download

expa82.co.cc/bl2/
Site loaded fine – no extra processes

1.oresmir.co.cc/1/load.php?spl=mdac
IE labeled download as unsafe – Saved and run successfully

marinada3.com/77/throatnut.php
Blocked by IE – Java exploit allowed to load – no additional processes

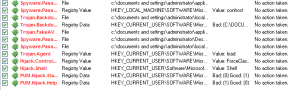
MSE found a few files it needed to send in for verification, but did not block anything.

Malwarebytes:
Objects infected: 12 (3 are non-infection related)

Verdict:
MSE didn’t actively block anything – it only found the files when I scanned the computer using MSE. I prefer a more active participant.
Test 7 (Microsoft Security Essentials MSE with TF):

Windows XP Pro SP3
Fully Updated 12.28.2010
Internet Explorer 8.0.6001.18702
Adobe Flash Player 10 ActiveX 10.1.102.64
Java 6 Update 23 6.0.230
Malwarebytes Anti-Malware 1.50.1.1100 5408
Threatfire 4.7.0.17

cryyahoo.info/tre/boba.exe
IE reported this site as BAD – File not found to download

expa82.co.cc/bl2/
Site loaded fine – no extra processes

1.oresmir.co.cc/1/load.php?spl=mdac
IE labeled download as unsafe – Threatfire blocked the installation

marinada3.com/77/throatnut.php
Blocked by IE – Threatfire blocked the java exploit from running

MSE, like in the previous test, did not block anything.

Malwarebytes:
Objects infected: 3 (3 are non-infection related)

Verdict:
MSE didn’t actively block anything – it only worked well with TF in finding new problem programs. I still prefer a more active participant, but MSE and TF worked well.

Final Results:
So it appears as though Threatfire really does help out. It also appears that Nod32 is only slightly better than McAfee and MSE edged them both out. McAfee did not find the infections on access or during a scan. Nod32 blocked only one file on access, but found nothing during a scan. MSE blocked nothing during on access, but found a couple files with issues during a scan.
I also realize that I didn’t include Adobe Reader as part of the package. Since I’ve already disposed of the virtual machines I don’t think I’ll go back and correct this error.

No AV – 11 infections
McAfee – 11 infections
Nod32 – 10 infections
MSE – 9 infections
McAfee with Threatfire – 1 infection
Nod32 with Threatfire – 0 infections
MSE with Threatfire – 0 infections

Final recommendation:
While I will continue to use Nod32 alongside Threatfire (I pay for the Nod32 subscription), and will continue to recommend it to my peers/clients, I must say that for the average home user MSE has come through with flying colors. However, when utilizing MSE you MUST scan your system after each download or on regular scanning intervals. Their lack of on-access scanning is my major gripe at this time.

FreeNAS Rebuilding

We decided to test pulling out a HD and sticking it back in to see how the FreeNAS would react.

Specs:
FreeNAS 0.7.2 (5543)
Areca ARC-1222 w/ Battery
Hotswap ICYDock drives
Hitachi 2TB SATA HD’s (QTY 8 )
RAID 50 (so a stripe of 2x RAID 5’s, 12TB unformatted)

Pulled out the HD, put the HD back in. Drive lights on 7 of the drives turned to orange (means data was being accessed/changed) and the drive we pulled out and put back was green (only power).

Logged into the Areca Web Panel and added the HD as a hot spare. The RAID controller instantly tried to rebuild the array. After 15 minutes the rebuild process was still at 0.0% so something was definitely wrong.

Checked the FreeNAS and HD space was rapidly being used up (about 100MB/sec). Checked “top” to see what the problem was – fsck_ufs was running full tilt.

FreeBSD was checking the HD for errors after a forced reboot earlier in the day. So there was little free time for the RAID controller to rebuild.

Unfortunately the kill PID command was not working. Kill -9 PID also failed. I would have to reboot.

Edit this file to make sure this doesn’t happen again:

vi /etc/rc.conf
i
background_fsck="NO"
Escape
:wq!

Reboot. Now, due to the HD’s being run full tilt, we had to manually reboot the server. It might have worked out OK if we just left it after issuing the reboot command, but I’m not a patient man.

Image For Linux

We’re using a utility called Image for Linux (IFL) to image systems (ghost/backup/whatever). It’s not free, but it’s not expensive either – and it works pretty well.

However, IFL uses nmblookup to connect to network shares. So, if you’re on a separate VLAN or network as your destination, you will not be able to find the storage device.

In my case I have a NAS on a 10.1.0.0/24 and the end users are on a 10.2.0.0/24 – with Layer 3 switches.

Boot off of IFL
Alt + F2
mkdir /mnt/share
/sbin/mount.cifs //servername_orip/sharename /mnt/share

Firefox Saved Password Retrieval

I sometimes save my password into firefox to make my life easier. Opera has a much better system for saving passwords, but I like my FF better.

I had a saved password and needed to retrieve the password (unmask it) for some documentation. Unfortunately I couldn’t remember which password I had used previously. Then I remembered a handy javascript that allows me to show the saved password.

Go to the site you want to retrieve the password
DO NOT login yet
Up at the address bar, overwrite what is there with:
javascript:(function(){var s,F,j,f,i; s = ""; F = document.forms; for(j=0; j

IIS 7.0 Admin Failed To Connect

I had a developer trying to connect to the admin panel of IIS7. They could open the MMC just fine, but when they clicked on the server (local server) it would give a failure:

There was an error connecting. Do you want to specify different credentials?

And then it would fail again.

Open a command prompt on the server:
%windir%\system32\inetsrv\appcmd list sites

So I edited the redirection.config file given, and found that one of the developers had put
Changed it to false, and yay it works! Oh, I had to close IIS Admin and reopen.

Install Nagiosgraph

Install NagiosGraph

First of all, this is running on Ubuntu 10.04.1 LTS x32. I installed Nagios 3.2.0 from the source packages (see another post on this site), and will be installing NagiosGraph 1.4.3. I’ve also installed Nagios-Plugins-1.4.15.

This will probably be a lot of writing, but in the end it was definitely worth my time.

Update System and Install SNMPD:

su root
apt-get install update
apt-get install upgrade
apt-get install snmpd
mv /etc/snmp/snmpd.conf /etc/snmp/snmpd.conf.org
nano /etc/snmp/snmpd.conf
rocommunity public
syslocation “MyLocation”
syscontact email@domain.tld
Save and close
nano /etc/default/snmpd
Change From:
# snmpd options (use syslog, close stdin/out/err).
SNMPDOPTS=’-Lsd -Lf /dev/null -u snmp -I -smux -p /var/run/snmpd.pid 127.0.0.1′
To:
# snmpd options (use syslog, close stdin/out/err).
#SNMPDOPTS=’-Lsd -Lf /dev/null -u snmp -I -smux -p /var/run/snmpd.pid 127.0.0.1′
SNMPDOPTS=’-Lsd -Lf /dev/null -u snmp -I -smux -p /var/run/snmpd.pid -c /etc/snmp/snmpd.conf’
Save and close
/etc/init.d/snmpd restart

Test SNMPD:

snmpwalk -v 1 -c public -O e IP_OF_YOUR_MACHINE
You can use Localhost (127.0.0.1) in lieu of another IP address

Download Required Files:

cd /home/nagios
wget http://voxel.dl.sourceforge.net/project/nagiosgraph/nagiosgraph/1.4.3/nagiosgraph-1.4.3.tar.gz
apt-get install rrdtool perl libcgi-pm-perl librrds-perl libgd-gd2-perl

Extract Required Files:

tar xzvf nagiosgraph-1.4.3.tar.gz
cd nagiosgraph-1.4.3

Copy Files:

mkdir /etc/nagiosgraph
cp etc/* /etc/nagiosgraph

Edit Perl Scripts With FilePath:

nano cgi/*.cgi lib/insert.pl
Find “use lib” line (definitely on the first page of text) and edit it to be /etc/nagiosgraph
Save all files

Continue Copying Files:

cp lib/insert.pl /usr/local/nagios/libexec
cp cgi/*.cgi /usr/local/nagios/sbin
cp share/nagiosgraph.css /usr/local/nagios/share
cp share/nagiosgraph.js /usr/local/nagios/share

Edit The Nagiosgraph.conf File:

nano /etc/nagiosgraph/nagiosgraph.conf
Set the following:
perflog = /var/nagios/perfdata.log
rrddir = /var/nagios/rrd
mapfile = /etc/nagiosgraph/map
nagiosgraphcgiurl = /nagios/cgi-bin
javascript = /nagios/nagiosgraph.js
stylesheet = /nagios/nagiosgraph.css
logfile = /var/log/nagiosgraph.log
cgilogfile = /var/log/nagiosgraph-cgi.log

Set Permissions For RRD Directory, Log Files, CGI Files:

mkdir /var/nagios/rrd
chown 777 /var/nagios
chown nagios /var/nagios/rrd
chmod 755 /var/nagios/rrd
touch /var/log/nagiosgraph.log
chown nagios /var/log/nagiosgraph.log
chmod 664 /var/log/nagiosgraph.log
touch /var/log/nagiosgraph-cgi.log
chown www-data /var/log/nagiosgraph-cgi.log
chmod 664 /var/log/nagiosgraph-cgi.log

Edit Nagios.cfg:

nano /usr/local/nagios/etc/nagios.cfg
process_performance_data=1
service_perfdata_file=/var/nagios/perfdata.log
service_perfdata_file_template=$LASTSERVICECHECK$||$HOSTNAME$||$SERVICEDESC$||$SERVICEOUTPUT$||$SERVICEPERFDATA$
service_perfdata_file_mode=a
service_perfdata_file_processing_interval=30
service_perfdata_file_processing_command=process-service-perfdata

Edit Commands.cfg (make sure this is enabled/correct):

nano /usr/local/nagios/etc/objects/commands.cfg
define command {
command_name process-service-perfdata
command_line /usr/local/nagios/libexec/insert.pl
}

Restart Nagios:

/etc/init.d/nagios restart

Edit Apache Configuration:

This was already done for me from the Nagios install, but just verify it’s correct.
nano /etc/apache2/conf.d/nagios.conf
ScriptAlias /nagios/cgi-bin /usr/local/nagios/sbin

# SSLRequireSSL
Options ExecCGI
AllowOverride None
Order allow,deny
Allow from all
# Order deny,allow
# Deny from all
# Allow from 127.0.0.1
AuthName “Nagios Access”
AuthType Basic
AuthUserFile /usr/local/nagios/etc/htpasswd.users
Require valid-user

There should be more below this, so just leave that alone.

Restart Apache:

apache2ctl restart

Test Your Site:

http://server/nagios/cgi-bin/show.cgi

You shouldn’t get any errors. If you get a 500 internal error, the issue is with Apache. If you get a “no rrd data found” error, then the configuration of nagiosgraph is incorrect OR you haven’t waited long enough.

You can try to run the script directly:

cd /usr/local/nagios/libexec
./insert.pl

Then verify that there is some data in the RRD directory:
ls /var/nagios/rrd/

To get it to work with Windows Clients:

Edit the map file:
nano /etc/nagiosgraph/map
Add the following to the END of the file:
# Service type: memory
# check command: check_nt -H Address -v MEMUSE -w 50 -c 90
#output: Memory usage: tootal:2467.75 Mb – used: 510.38 Mb (21%) – free: 1957.37 Mb (79%)
/perfdata:Memory usage=([.0-9])+Mb;([.0-9+);([.0-9+);([.0-9+);([.0-9]+)/
and push @s, [ntmem,
[memused, GAUGE, $1*1024**2 ]
];
# Service type: ntload
# Check command: check_nt -H Address -v CPULOAD -l1,70,90,5,70,90,30,70,90
# output: CPU Load 9% (5 min average) 11% (30 min average)
#perfdata: ‘5 min avg Load’=9%;70;80;0;100 ’30 min avg Load’=11%;70;90;0;100
/output:.*?(\d+)% .*?(\d+)% /
and push @s, [ ntload,
[ avg05min, GAUGE, $1 ],
[avg30min, GAUGE, $2 ] ];
# Service type: ntdisk
# check command: check_nt -H Address -v USEDDISKSPACE -lc -w 75 -c 90
# output: c:\ – total: 25.87 Gb – used: 4.10 Gb (16%) – free 21.77 Gb (84%)
# perfdata: c:\ Used Space=4.10Gb;19.40;23.28;0.00;25.87
/perfdata:.*Space=([.0-9]+)Gb;([.0-9]+);([.0-9]+);([.0-9]+);([.0-9]+)/
and push @s, [ ntdisk,
[ diskused, GAUGE, $1*1024**3 ],
[ diskwarn, GAUGE, $2*1024**3 ],
[ diskcrit, GAUGE, $3*1024**3 ],
[ diskmaxi, GAUGE, $5*1024**3 ] ];

Save and close the file, then restart nagios (/etc/init.d/nagios restart)

***EDIT***
Updated – had “.conf” instead of “.cfg” under “edit nagios.cfg”
Added chmod 777 for /var/nagios to allow perfdata.log to be written

Ramblings Of An IT Person